
Zero Trust Maturity Model Resource Center
Purpose of this page
- A plain-language overview of CISA’s Zero Trust Maturity Model (ZTMM)
- Free interactive spreadsheets to self-assess your organization’s maturity
- Quick Links
Security leaders often need practical guidance on applying the CISA Zero Trust Maturity Model within their own organizations. This site is created and maintained by Numberline Security to provide that guidance.
Zero Trust Maturity Models : Overview
Zero Trust is an ongoing journey, not a one-time implementation. Organizations need a reference point to identify their current state and their target state. A Zero Trust Maturity Model (ZTMM) provides this reference point. Completing a maturity self-assessment is a recommended first step for organizations beginning a Zero Trust journey, and is mandatory for US Federal Agencies.
The CISA Zero Trust Maturity Model
Multiple Zero Trust Maturity Models exist. The most widely referenced model is published by the U.S. Cybersecurity and Infrastructure Security Agency (CISA). Key facts about this model:
- CISA released the first draft for public comment in June 2021, finalized in August 2021
- CISA published version 2.0 in April 2023, which remains the current version
- The full CISA Zero Trust Maturity Model is available at: https://www.cisa.gov/zero-trust-maturity-model
The CISA model is widely adopted across the cybersecurity industry and functions as a common baseline vocabulary and framework for Zero Trust. This page explains how to best use it, and introduces the free supporting tools provided by Numberline.
CISA Zero Trust 5 Pillars
The CISA Zero Trust Maturity Model introduces five pillars, three cross-cutting capabilities, and four maturity levels, shown in the image below.
CISA Zero Trust Maturity Model
CISA’s Zero Trust Maturity Model is built around five pillars, as shown above: Identity, Devices, Networks, Applications and Workloads, and Data. Each of these pillars progresses through four maturity stages: Traditional, Initial, Advanced, and Optimal. Layered across all five pillars are three cross-cutting capabilities, Visibility and Analytics, Automation and Orchestration, and Governance, which support and enable maturity within each pillar. Figure 4 below summarizes what each pillar looks like at every maturity stage, giving organizations a high-level view of the full model before drilling into the specifics of any one pillar or capability.
Identity
Devices
Networks
Applications and Workloads
Data
- Continuous validation and risk analysis
- Enterprise-wide identity integration
- Tailored, as-needed automated access
- Continuous physical and virtual asset analysis including automated supply chain risk management and integrated threat protections
- Resource access depends on real-time device risk analytics
- Distributed micro-perimeters with just-in-time and just-enough access controls and proportionate resilience
- Configurations evolve to meet application profile needs
- Integrates best practices for cryptographic agility
- Applications available over public networks with continuously authorized access
- Protections against sophisticated attacks in all workflows
- Immutable workloads with security testing integrated throughout lifecycle
- Continuous data inventorying
- Automated data categorization and labeling enterprise-wide
- Optimized data availability
- DLP exfil blocking
- Dynamic access controls
- Encrypts data in use
- Phishing-resistant MFA
- Consolidation and secure integration of identity stores
- Automated identity risk assessments
- Need/session-based access
- Most physical and virtual assets are tracked
- Enforced compliance implemented with integrated threat protections
- Initial resource access depends on device posture
- Expanded isolation and resilience mechanisms
- Configurations adapt based on automated risk-aware application profile assessments
- Encrypts applicable network traffic and manages issuance and rotation of keys
- Most mission critical applications available over public networks to authorized users
- Protections integrated in all application workflows with context-based access controls
- Coordinated teams for development, security, and operations
- Consistent, tiered, targeted categorization and labeling
- Redundant, highly available data stores
- Static DLP
- Automated context-based access
- Encrypts data at rest
- MFA with passwords
- Self-managed and hosted identity stores
- Manual identity risk assessments
- Access expires with automated review
- All physical assets tracked
- Limited device-based access control and compliance enforcement
- Some protections delivered via automation
- Initial isolation of critical workloads
- Network capabilities manage availability demands for more applications
- Dynamic configurations for some portions of the network
- Encrypt more traffic and formalize key management policies
- Some mission critical workflows have integrated protections and are accessible over public networks to authorized users
- Formal code deployment mechanisms through CI/CD pipelines
- Static and dynamic security testing prior to deployment
- Limited automation to inventory data and control access
- Begin to implement a strategy for data categorization
- Some highly available data stores
- Encrypts data in transit
- Initial centralized key management policies
- Passwords or MFA
- On-premises identity stores
- Limited identity risk assessments
- Permanent access with periodic review
- Manually tracking device inventory
- Limited compliance visibility
- No device criteria for resource access
- Manual deployment of threat protections to some devices
- Large perimeter/macro-segmentation
- Limited resilience and manually managed rulesets and configurations
- Minimal traffic encryption with ad hoc key management
- Mission critical applications accessible via private networks
- Protections have minimal workflow integration
- Ad hoc development, testing, and production environments
- Manually inventory and categorize data
- On-prem data stores
- Static access controls
- Minimal encryption of data at rest and in transit with ad hoc key management
High-Level Zero Trust Maturity Model Overview (Source: CISA Zero Trust Maturity Model v2.0)
Assessing Your Maturity
CISAs model is built on a detailed set of approximately 40 functions that they’ve defined across the five pillars, and for each of these they’ve provided a description of at each level of maturity.
Zero Trust Maturity Model
Five pillars, each with its own functions, all resting on three capabilities that span every pillar.
Identity
- Authentication
- Identity Stores
- Risk Assessments
- Access Management
Devices
- Policy Enforcement & Compliance Monitoring
- Asset & Supply Chain Risk Management
- Resource Access
- Device Threat Protection
Networks
- Network Segmentation
- Network Traffic Management
- Traffic Encryption
- Network Resilience
Applications & Workloads
- Application Access
- Application Threat Protections
- Accessible Applications
- Secure Application Development & Deployment Workflow
- Application Security Testing
Data
- Data Inventory Management
- Data Categorization
- Data Availability
- Data Access
- Data Encryption
For example, the Network Segmentation function maturity levels are defined as follows:
Network Segmentation
Networks pillar maturity progression-
Traditional
Agency defines their network architecture using large perimeter/macro-segmentation with minimal restrictions on reachability within network segments. Agency may also rely on multi-service interconnections (e.g., bulk traffic VPN tunnels).
-
Initial
Agency begins to deploy network architecture with the isolation of critical workloads, constraining connectivity to least function principles, and a transition toward service-specific interconnections.
-
Advanced
Agency expands deployment of endpoint and application profile isolation mechanisms to more of their network architecture with ingress/egress micro-perimeters and service-specific interconnections.
-
Optimal
Agency network architecture consists of fully distributed ingress/egress micro-perimeters and extensive micro-segmentation based around application profiles with dynamic just-in-time and just-enough connectivity for service-specific interconnections.
As such, this detailed view represents the best starting point by which organizations can perform a Zero Trust self-assessment, and is the model for which we’ve created an interactive spreadsheet, described below.
Start with CISA, go further with ZTMM+
The CISA model is a strong foundation and a great place to start your Zero Trust self-assessment. But it has gaps when applied outside the federal space, and is getting a bit dated. Numberline Security built ZTMM+, an enhanced and extended version of the CISA model, from our experience running maturity assessments in both the private and public sectors. Within ZTMM+, we
- Provided definitions for all 40 pillar functions, which are missing from the CISA model
- Redefines maturity levels for 15 functions to fit the way enterprises actually operate
- Adds 8 new functions covering areas the original model misses
- Includes a structured assessment methodology, so you can measure maturity consistently and act on the results
Learn more about ZTMM+ here.
Want to use the original CISA ZTMM? Learn about our free spreadsheet below to assess your organization against the CISA model today.
CISA Zero Trust Maturity Model Spreadsheet Tool
Numberline Security has developed a free, interactive spreadsheet version of the CISA Zero Trust Maturity Model. Instead of reading through static tables, you can assess your organization’s maturity interactively: select a level for each function and watch your results update automatically.
The Google Sheet is read-only; choose File → Make a copy to use it.
For Excel, download the Excel file using the link above. Exporting the Google Sheet as Excel will cause errors in the formatting and formulas.
The spreadsheet contains the following tabs:
Introduction
Start here. This worksheet covers:
- An overview of the spreadsheet and how it maps to the CISA model
- Step-by-step instructions for completing your self-assessment
- Details of the formulas behind the automatic shading
Select a tab above to preview each worksheet.
CISA Zero Trust Maturity Model
All 40 functions and their maturity levels in a plain-text table, ready to copy, edit, and adapt for your organization.
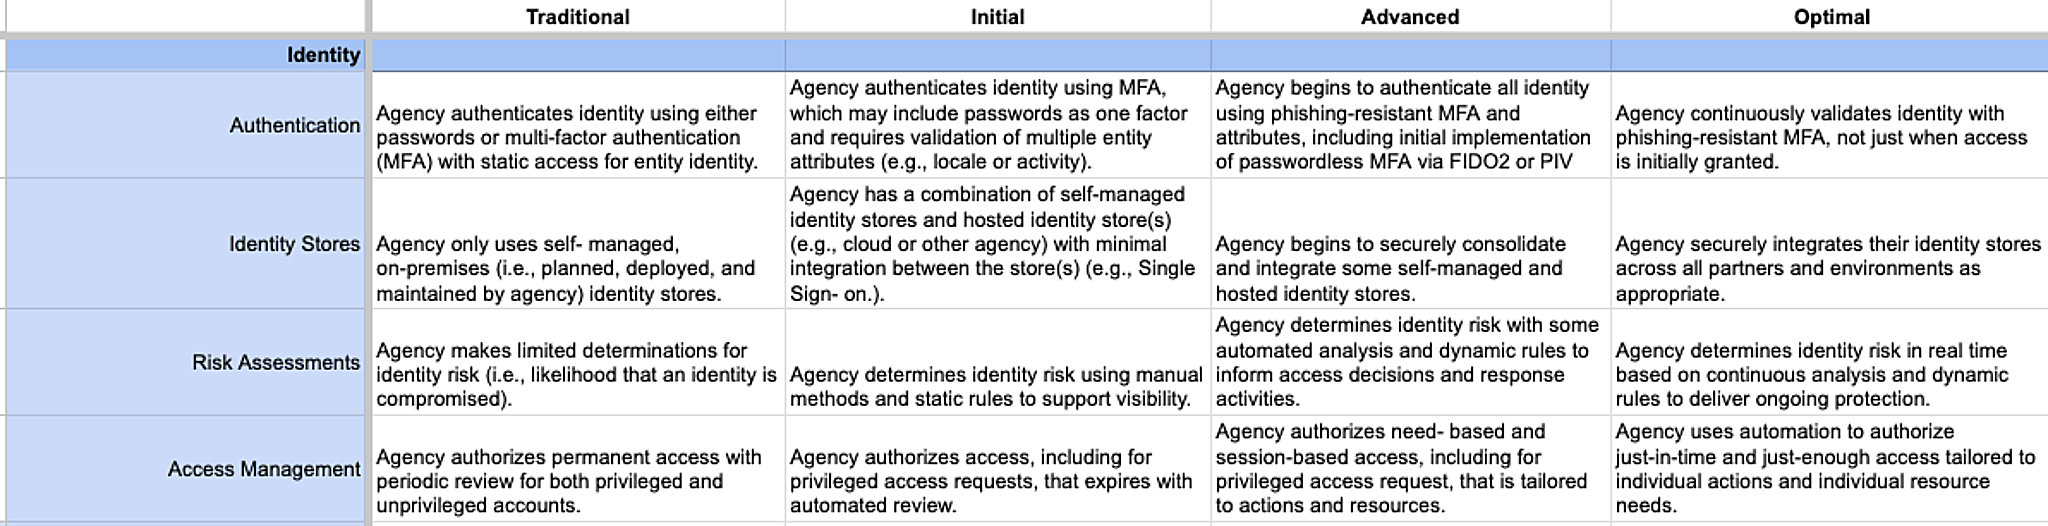
Click any image to view it full size.
Interactive
Self-assess your organization one function at a time. We’ve added Unknown to CISA’s four levels for areas where you don’t yet have enough information to decide.

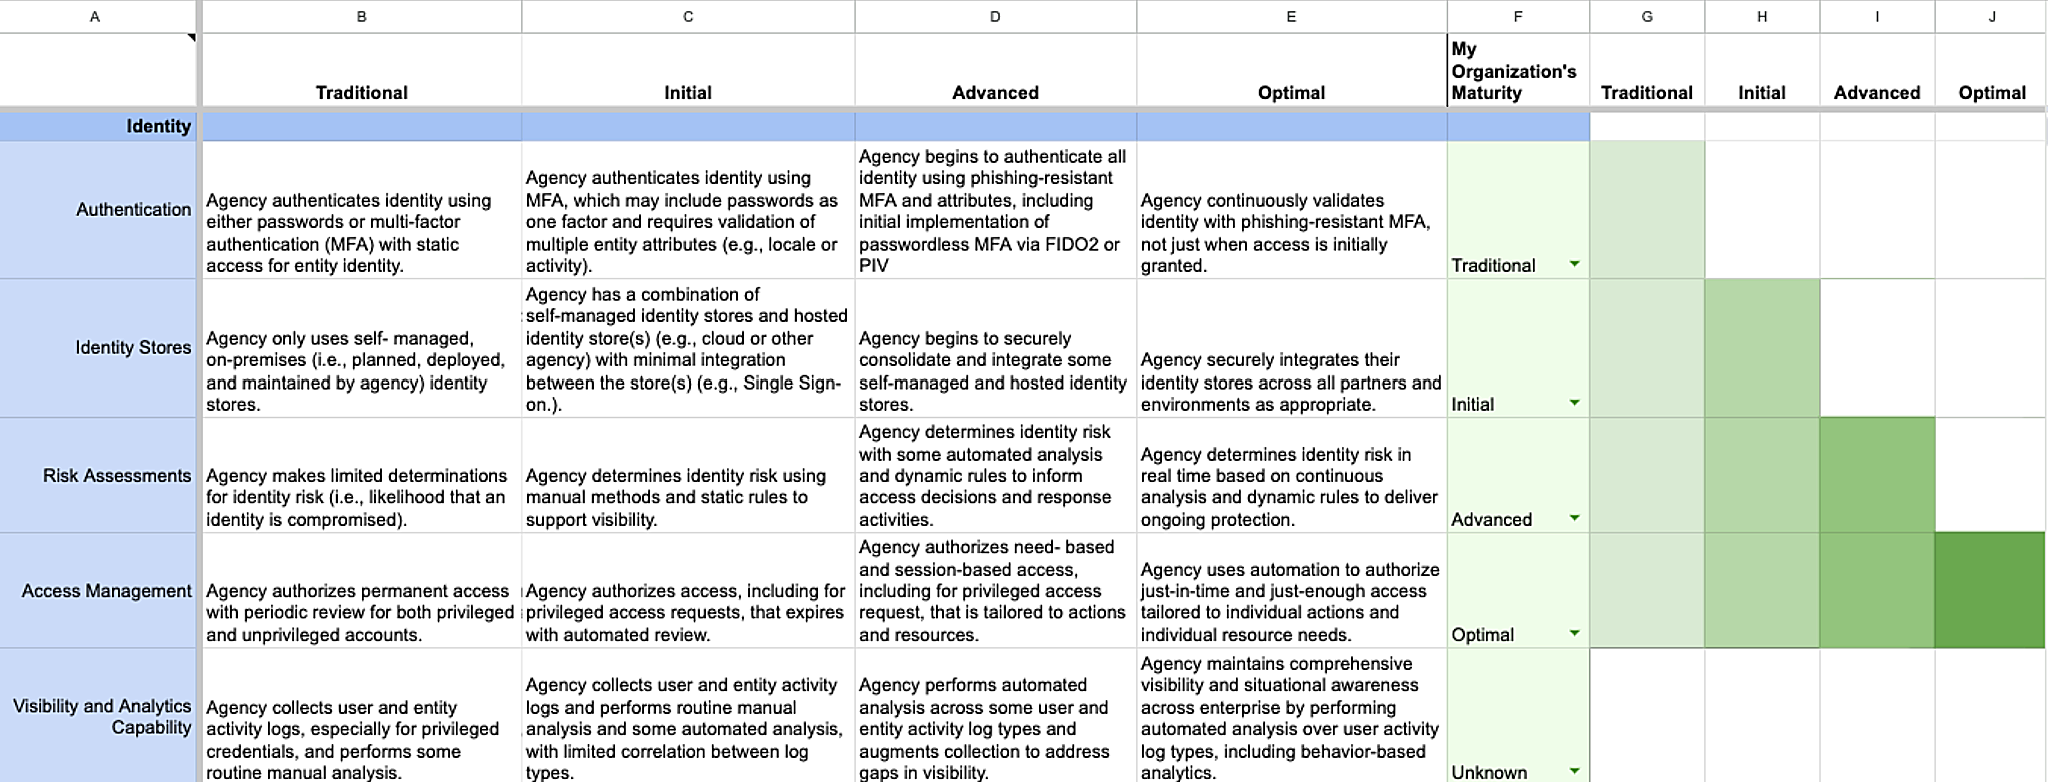
Click any image to view it full size.
Maturity Model Assessment
A compact summary of your results, formatted for easy viewing and sharing. It updates automatically from the Interactive worksheet, and functions marked Unknown stay unshaded.

Click any image to view it full size.
Is this applicable to Enterprises (Non-Federal Agencies)?
Yes. The CISA Zero Trust Maturity Model (ZTMM) was written for U.S. federal agencies, so it uses phrases like “Agencies should…” throughout. But CISA makes clear that it isn’t only for government. In its introduction, the model states: “While the ZTMM is specifically tailored for federal agencies… all organizations should review and consider adoption of the approaches outlined in this document.” (Emphasis ours.)
In practice, enterprises and other organizations can apply the model by reading “agency” as “enterprise” or “organization.”
Other Zero Trust Maturity Models
The CISA model has become the most widely used vendor-neutral Zero Trust maturity model, but it isn’t the only one worth knowing.
U.S. Department of War
The DoW has published its own Zero Trust guidance for defense organizations:
- Zero Trust Reference Architecture, which includes a maturity model
- DoD Zero Trust Strategy, which defines the DoD’s pillars
Vendor models
Several security vendors have published their own Zero Trust maturity models. They can be useful references, but none has achieved widespread industry adoption.
Numberline ZTMM+
Our enhanced version of the CISA model, built for enterprises. ZTMM+ defines all 40 functions, refines maturity levels for enterprise environments, adds new functions, and includes a structured assessment methodology.
Explore ZTMM+Questions?
We’d love to hear how you’re using the spreadsheet and what would make it better.